Michael Barisua Madu
Professional Profile
Practicing Company Meat Inspector with comprehensive experience enforcing food safety regulations, standard operating procedures, and Risk Management Programmes (RMPs) across both multi-species lines (sheep, lamb, bobby calf) and dedicated beef processing facilities. Uniquely backed by a professional background in IT systems administration, cybersecurity, and digital access control within regulated environments.
Areas of Expertise
Compliance & Food Safety
- Multi-Species Processing (Beef, Sheep, Lamb, Calf)
- Regulatory Compliance (Animal Products Act)
- HACCP & Risk Management Programmes (RMPs)
- ISO 22000 / ISO 9001 Systems Alignment
- Audit Readiness & Documentation Control
IT & Systems Security
- Active Directory & Microsoft 365 / Entra ID
- Network Security (Splunk, Wireshark, Nmap)
- ERP Fundamentals (SAP Materials Management)
- Access Control & Incident Response
Home Lab Projects
Self-directed infrastructure builds — real environments configured, broken, troubleshot, and documented end to end. Part of a 7-lab IT/cybersecurity series running through December 2026.
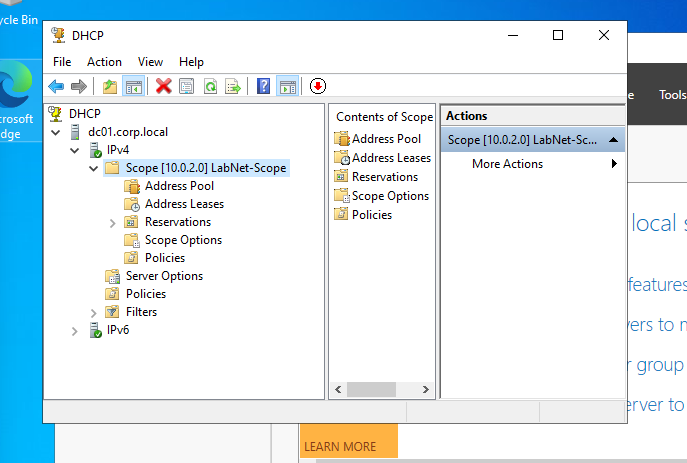
Active Directory & Windows Server Home Lab
Built a full AD domain in VirtualBox — domain controller, OU/group structure, Group Policy (password policy, drive mapping, restrictions), DNS, DHCP, NTFS/share permissions, and a domain-joined Windows 11 client. Verified end-to-end with real troubleshooting documented.
View on GitHub →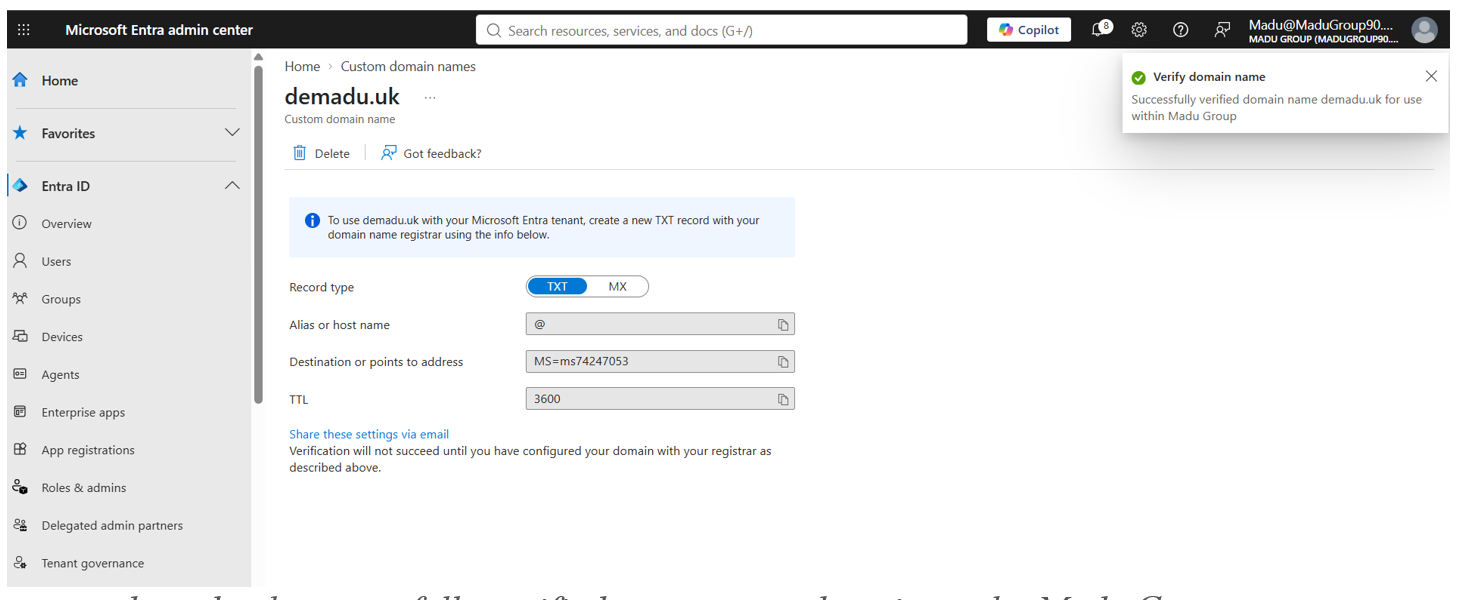
Microsoft 365 / Entra ID Lab
Cloud identity and access management on a Microsoft Entra ID tenant with a verified custom domain — department-based security groups, a Conditional Access policy requiring MFA for higher-risk staff (tested in report-only mode), and RBAC delegation of user administration away from the Global Admin account.
View on GitHub →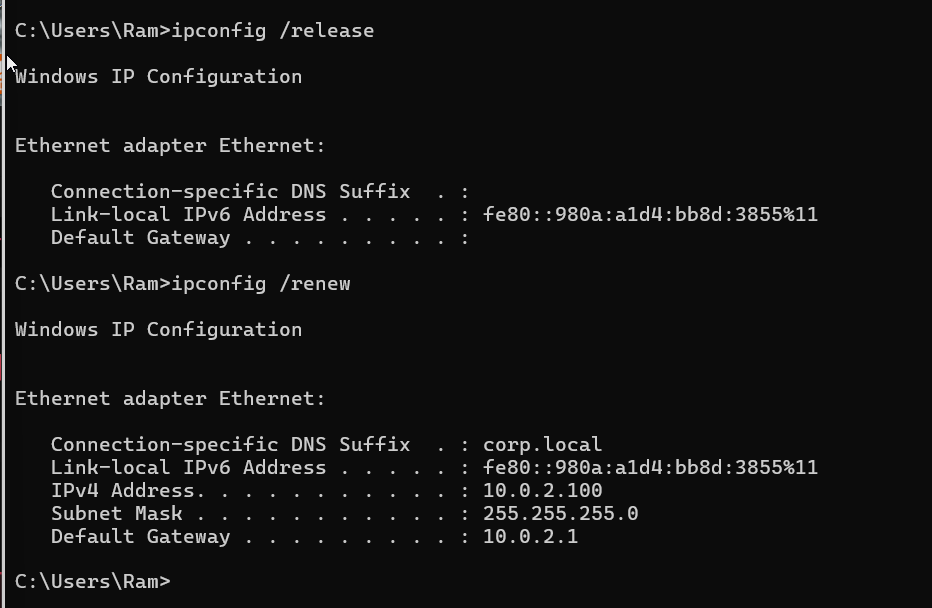
Networking Lab
VLANs, DHCP/DNS, firewall rules, routing, and Wireshark packet analysis — building and troubleshooting a segmented network from scratch.
Repo coming soon →Work History
- Execute precision processing operations on high-throughput beef slaughter lines in strict alignment with site standard operating procedures (SOPs).
- Uphold absolute structural compliance with New Zealand food safety legislation and rigorous beef carcass dressing hygiene parameters.
- Maintain close communication with QA and inspection teams to ensure continuous execution of Zero Faecal Tolerance (ZFT) protocols.
- Verified compliance with New Zealand food safety and export regulatory frameworks, specifically managing sheep, lamb, and bobby calf multi-species lines.
- Conducted strict verification activities across slaughter and processing operations, adhering to Zero Faecal Tolerance (ZFT) standards and HACCP principles under the Animal Products Act.
- Maintained accurate, traceable inspection records and audit evidence in line with ISO 9001 and ISO 22000 documentation principles.
- Supported ongoing audit readiness for internal reviews and external regulatory verification bodies.
- Supported compliance operations within a regulated healthcare environment governed by strict data protection and HIPAA-aligned privacy principles.
- Maintained controlled user access to sensitive hospital systems, managed role-based permissions, and supported internal audit tracks.
- Participated in regular risk assessments, incident reporting, and corrective action logging to guarantee documentation accuracy and traceability.
- Managed deployment and network configuration updates across site-wide terminal systems to ensure infrastructure reliability.
- Administered Active Directory access parameters, auditing user groups to prevent unauthorized privilege creep.
- Delivered fast-turnaround technical incident mitigation, keeping network downtime to an absolute minimum.
Education & Certifications
Qualifications & Credentials
- Bachelor of Science in Computer Science
University of the People - NZ Certificate in Meat Processing (Level 4)
Compliance & Quality Assurance - ISC2: Certified in Cybersecurity (CC)
- Google: IT Support Professional Certificate
- Cisco: Introduction to Cybersecurity
- US DHS: Advanced Cybersecurity for Industrial Control Systems (ICS)
Practical Industry Simulations
Hands-on technical workflows completed via Forage architecture:
- Telstra & AIG: Enterprise Incident Response & Ransomware Mitigation
- Datacom & ANZ: APT Impact Analysis & Cyber Risk Governance Frameworks
- Mastercard: Phishing Simulation Design & Behavioral Data Interpretation
- J.P. Morgan Chase: Application Security Fundamentals & Fraud Data Analysis
Technical Projects & Simulations
Enterprise Incident Response & Threat Mitigation
Simulations: Telstra, AIG (Shields Up)
- Simulated end-to-end incident response for active malware attacks; analyzed attack vectors, conducted post-mortem isolation, and engineered strategies to bypass active ransomware.
- Developed and deployed rapid patching strategies to counter critical zero-day exploits within production environments, minimizing potential downtime.
Cyber Risk Governance & Threat Intelligence
Simulations: Datacom, ANZ, Mastercard
- Analyzed the systemic impact of Advanced Persistent Threat (APT) breaches on enterprise information security architectures.
- Formulated comprehensive cybersecurity risk assessment frameworks to identify operational vulnerabilities and align security postures with business objectives.
- Conducted digital and social engineering investigations; designed corporate phishing email simulations and interpreted behavioral data to improve organizational security awareness.
Application Security & Data Integrity
Simulations: J.P. Morgan Chase & Co.
- Designed and developed secure access management systems to tighten control over sensitive enterprise information, preventing unauthorized privilege creep.
- Analyzed large, complex datasets of financial payment services to detect anomalies and flag fraudulent activity.
- Applied application security fundamentals to web environments and engineered machine learning email classifiers (Spam vs. Ham) to mitigate inbound vector threats.